
Set up Single Sign-On (SSO)
Configure Single Sign-On with Okta, Auth0, or Microsoft Entra ID so your team signs in using existing accounts without creating new passwords.
Single Sign-On (SSO) lets your team sign in with an existing account from an identity provider, without setting a password in awork.
SSO is only available on the awork Enterprise plan.
Important: awork does not support SAML 2.0. Instead, awork uses the OpenID Connect standard based on OAuth 2.0.
Main benefits and use cases
SSO makes signing in simple and consistent:
- Let team members use their existing identity provider accounts instead of creating a new awork password
- Use a modern OpenID Connect login based on OAuth 2.0
- Optionally disable other sign-in methods once SSO is set up
How to set up Single Sign-On (SSO)
Choose a supported identity provider
Supported identity providers include:
- Okta (website)
- Auth0 (website)
- Microsoft Entra ID (formerly Azure AD) (website)
- OneLogin (website)
- GSuite (Google IAM: website)
- Keycloak (website)
If your identity provider isn't listed, contact us through Support and we'll look into connecting it.
Set up SSO in awork
- Go to Einstellungen (the gear icon at the bottom left of the main menu) > Integrationen
- Open the Integrations-Bibliothek and select the provider you want
- Fill in the fields shown and complete the setup
Note: Subdomain refers to your provider's subdomain, not your awork workspace URL.
Allow the required redirect URLs
The following redirect URLs must be allowed:
https://app.awork.com/enterprise-login https://app.awork.com/api/v1/accounts/authorize-slack https://app.awork.com/api/v1/accounts/external/{Name des Login Providers}
https://app.awork.com/api/v1/accounts/msteams/authorize https://app.awork.com/api/v1/accounts/authorize
Service-specific redirect URLs:
- Web login:
https://app.awork.com/enterprise-login - Slack authorization:
https://app.awork.com/api/v1/accounts/authorize-slack - Microsoft Teams authorization:
https://app.awork.com/api/v1/accounts/msteams/authorize - Zapier:
https://app.awork.com/api/v1/accounts/authorize
Configure SSO via Okta
- Open the Okta configuration at YOUR-SUBDOMAIN.okta.com/admin
- In the menu, go to the Applications section
- Add a new application and name it, for example, awork
- Copy the Client-ID, Client-Secret, and Subdomain into the awork configuration, then save using Speichern
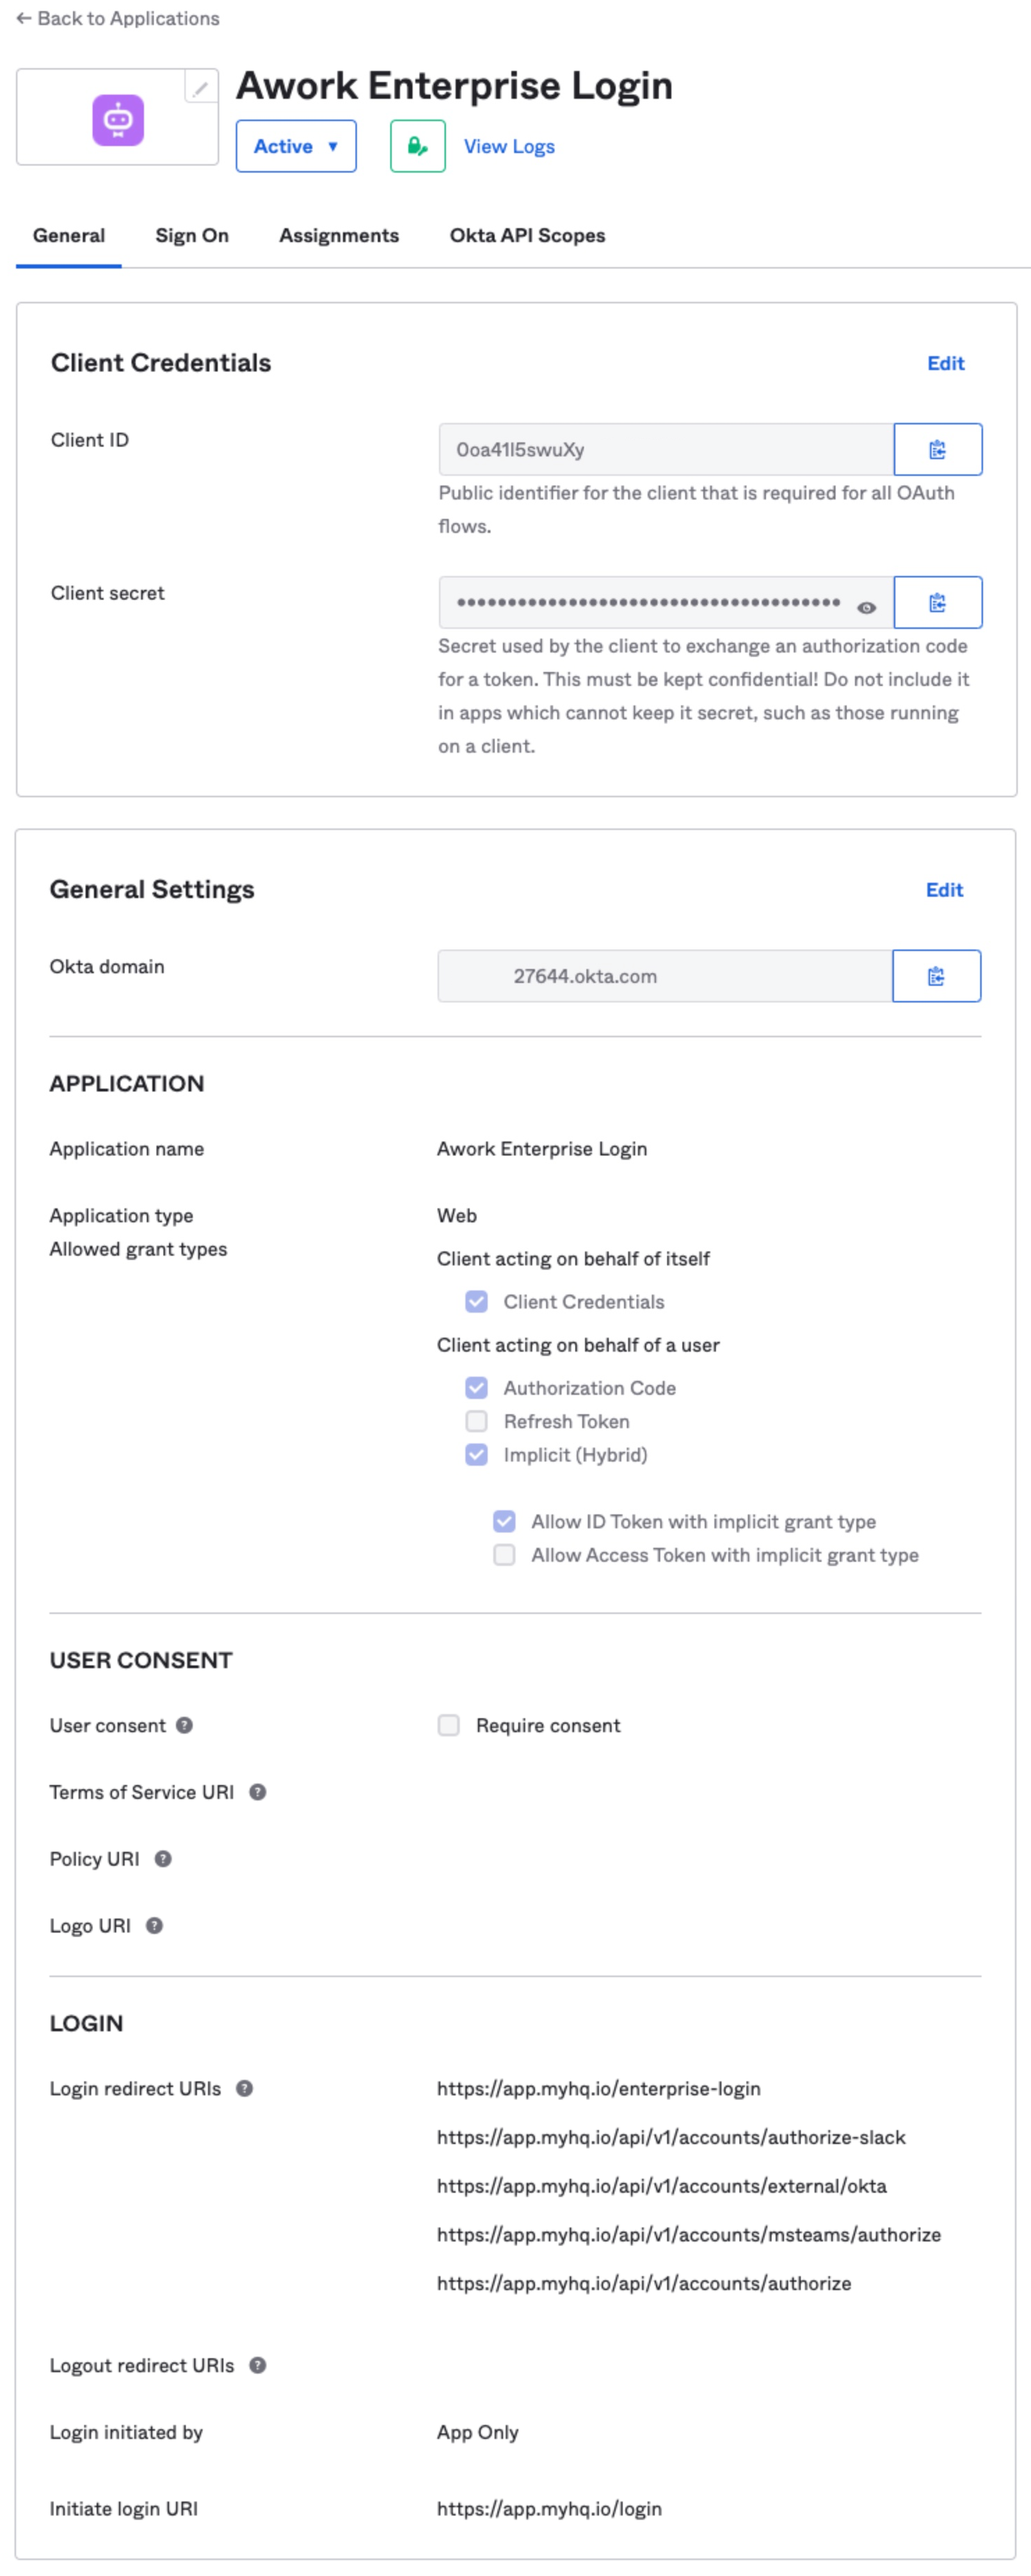
Important: Set up the Login Redirect-URLs correctly, or Okta won't be able to redirect users properly. The Implicit (Hybrid) Flow (including the ID Token grant type) must be enabled. User consent isn't required because awork only accesses the user's name and email address when they sign in.
In Okta, also set the following in the Login section:
- Initiate login URI: AWORK_SUBDOMAIN.awork.com/login
- Login redirect URIs: https://app.awork.com/enterprise-login https://app.awork.com/api/v1/accounts/authorize-slack https://app.awork.com/api/v1/accounts/external/okta https://app.awork.com/api/v1/accounts/msteams/authorize https://app.awork.com/api/v1/accounts/authorize
 )
Configure SSO with Auth0
- Open the Auth0 configuration
- In the menu, go to the Applications section
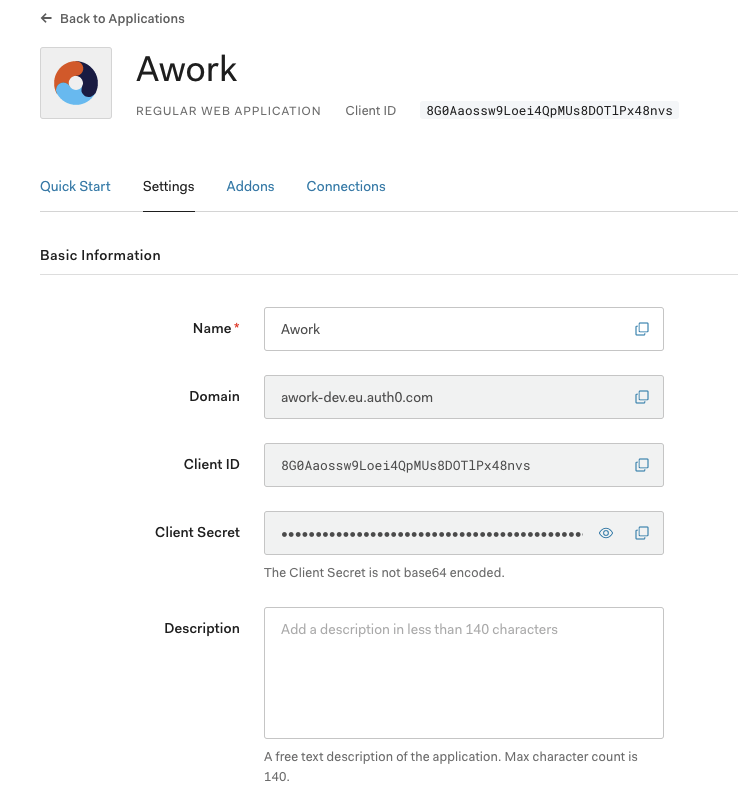
- Add a new application of type Regular Web Applications and name it, for example, awork
- Copy the Client-ID, Client-Secret, and Subdomain into the awork configuration and save
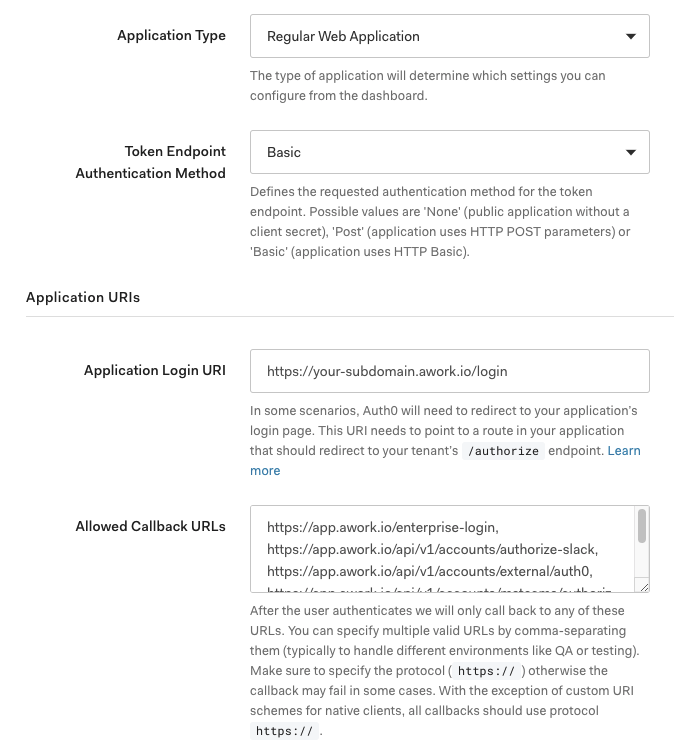
- Set the following URLs in the Application URLs section:
- Application login URL: AWORK_SUBDOMAIN.awork.com/login
- Allowed callback URLs: https://app.awork.com/enterprise-login, https://app.awork.com/api/v1/accounts/authorize-slack, https://app.awork.com/api/v1/accounts/external/auth0, https://app.awork.com/api/v1/accounts/msteams/authorize, https://app.awork.com/api/v1/accounts/authorize
- Allowed web origins: AWORK_SUBDOMAIN.awork.com app.awork.com
Note: All other settings are already configured correctly by default.
 )
 )
Configure SSO with OneLogin
- Open the OneLogin configuration at SUBDOMAIN.onelogin.com
- In the menu, go to the Applications section
- Add a new application by clicking Add App in the top right, and name it, for example, awork
- Choose OpenID Connect (OIDC) as the type, give it a name such as awork, and save
- You'll find the Client-ID and Client-Secret in the SSO section. You can find the Subdomain in your OneLogin account URL ({Subdomain}.onelogin.com). Enter these values in awork and save
- Set the following URLs in the Configuration section:
- Login URL: AWORK_SUBDOMAIN.awork.com/login
- Redirect URIs: https://app.awork.com/enterprise-login https://app.awork.com/api/v1/accounts/authorize-slack https://app.awork.com/api/v1/accounts/external/onelogin https://app.awork.com/api/v1/accounts/msteams/authorize https://app.awork.com/api/v1/accounts/authorize
Configure SSO with Microsoft Entra ID (formerly Azure AD)
-
Open the Entra ID configuration in the Azure portal
-
In the menu, under Manage, click App-Registrierungen
-
Add a new registration and name it, for example, awork SSO
-
Set Unterstützte Kontotypen to Nur Konten in diesem Organisationsverzeichnis (nur "deine Domain" - einzelner Mandant) and enter
https://app.awork.com/enterprise-loginas the redirect URI for the Web platform. Then click Registrieren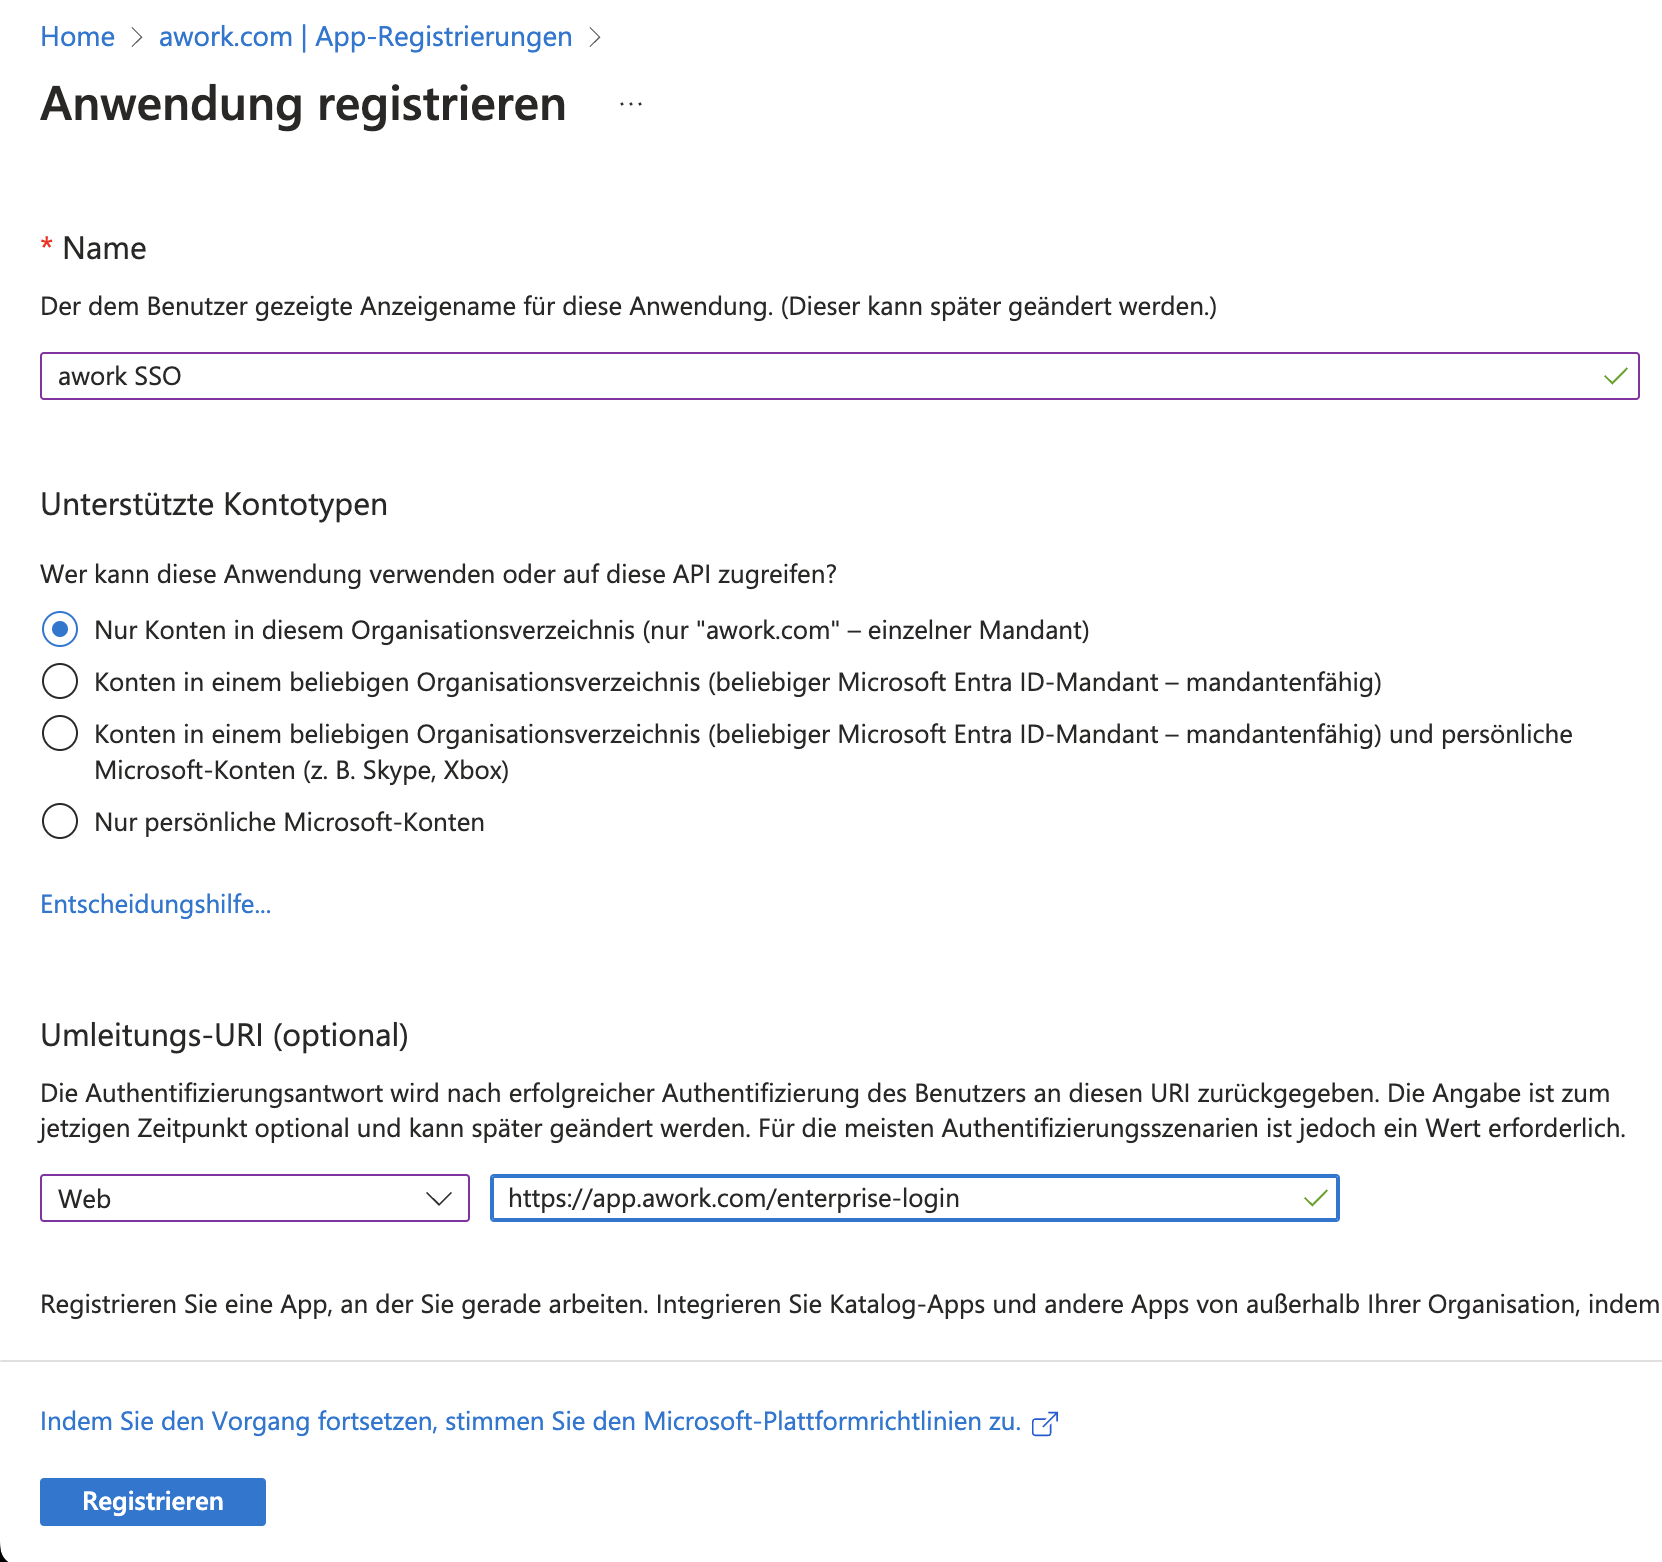 )
-
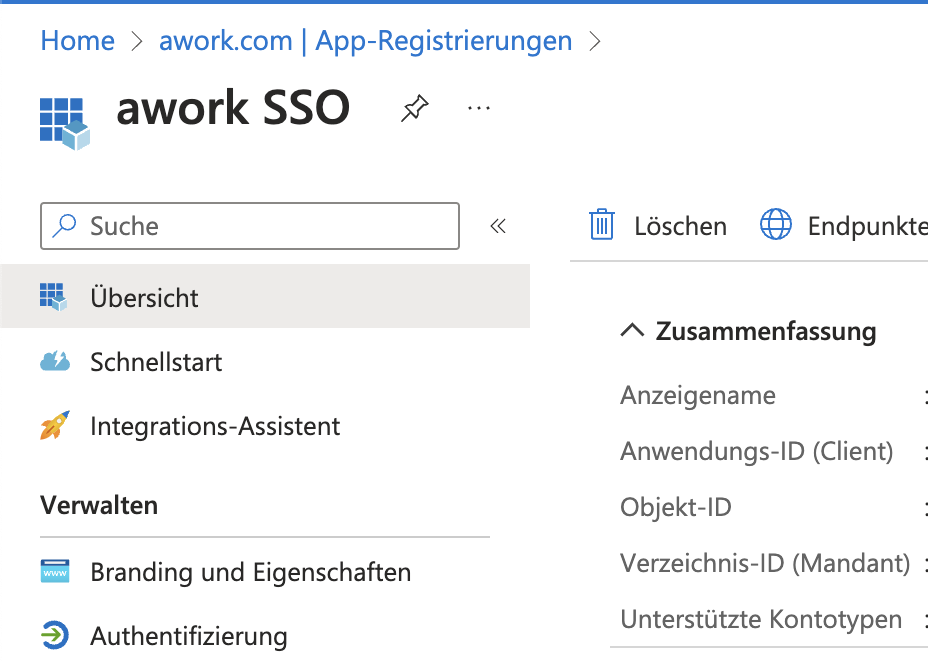
In the Übersicht, you'll find the Anwendungs-ID (Client) (= Client Id in awork) and the Verzeichnis-ID (Mandant) (= Subdomain in awork)
 )
-
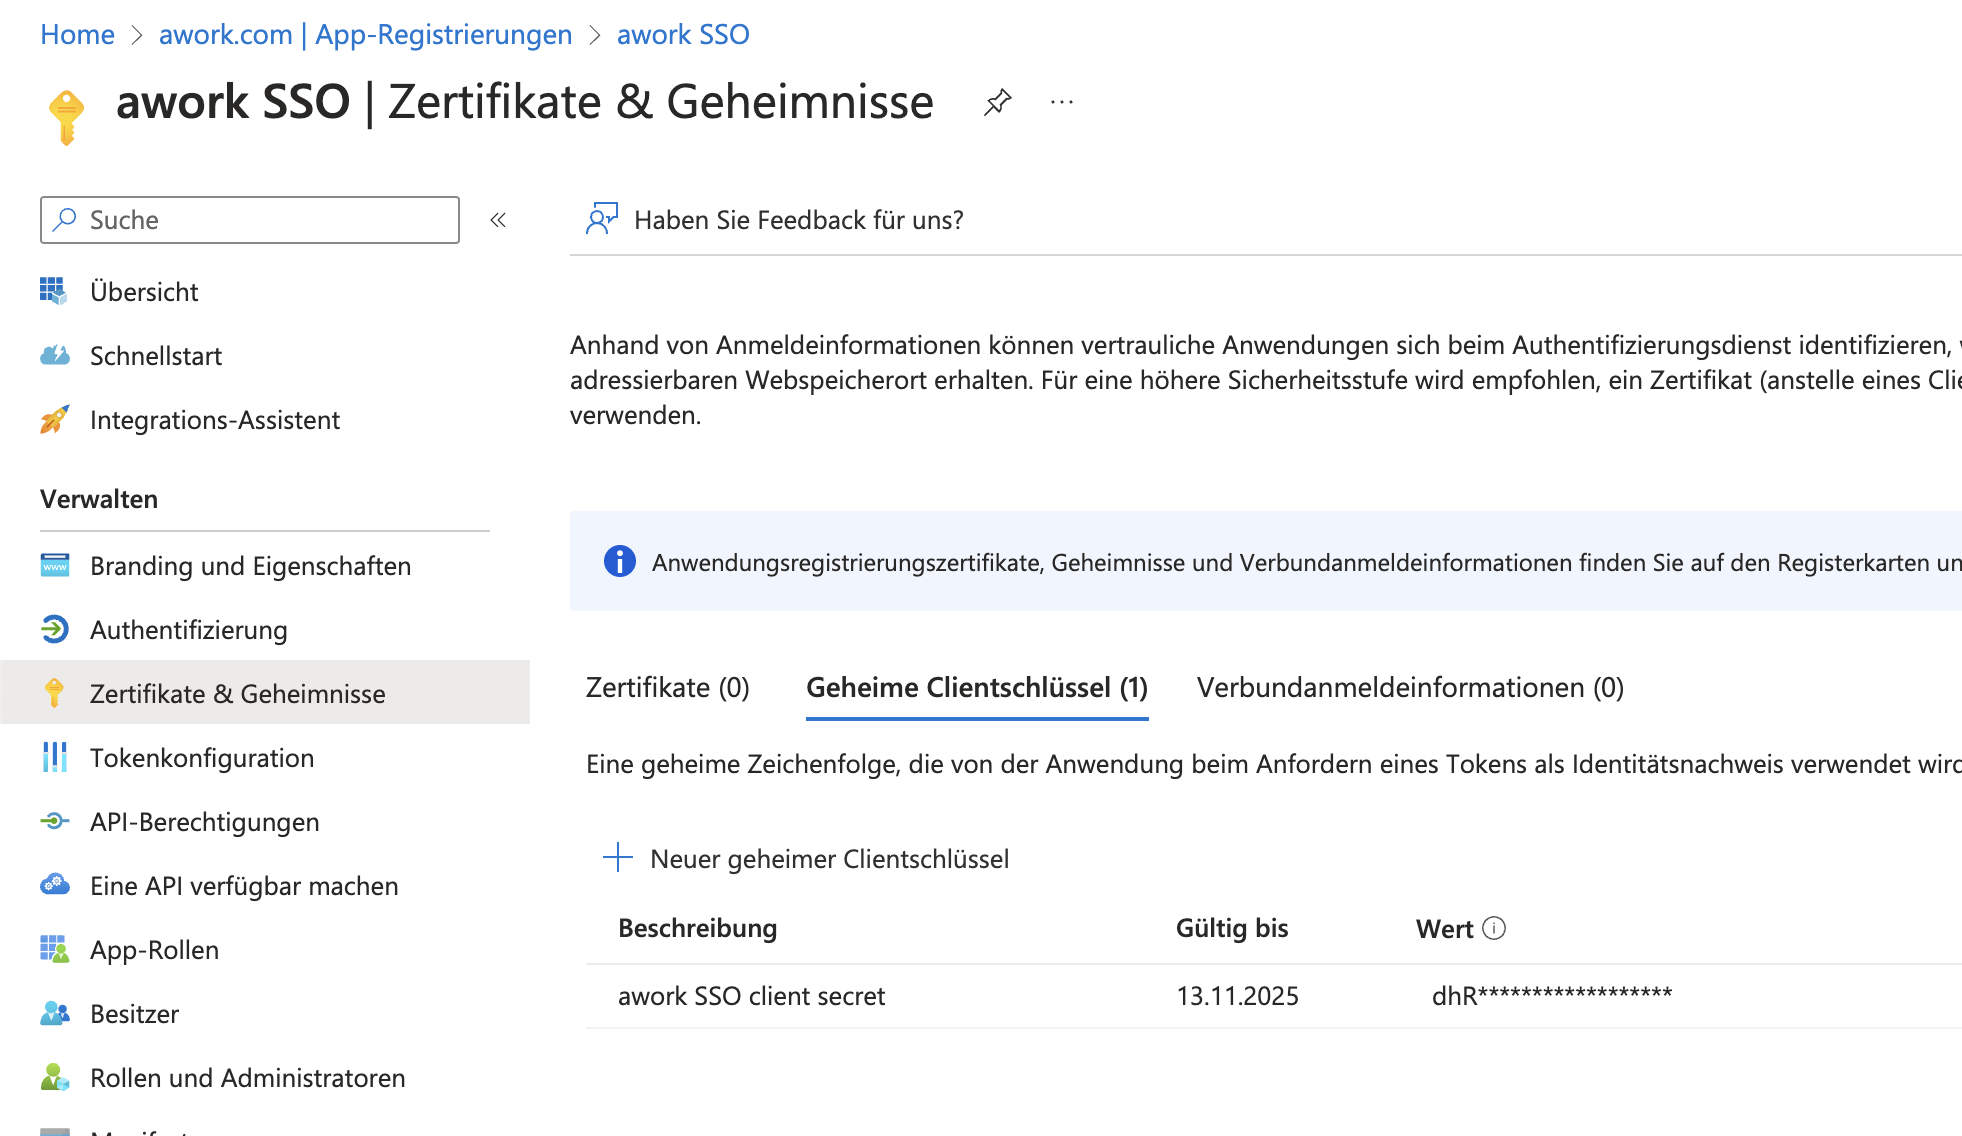
Under Zertifikate und Geheimnisse, you can create a new Geheimen Clientschlüssel and enter its value in awork as the Client Secret.
Important: Copy the value, not the Secret ID.
 )
To rotate client secrets, you need to delete the SSO integration in awork and add it again with the new secret.
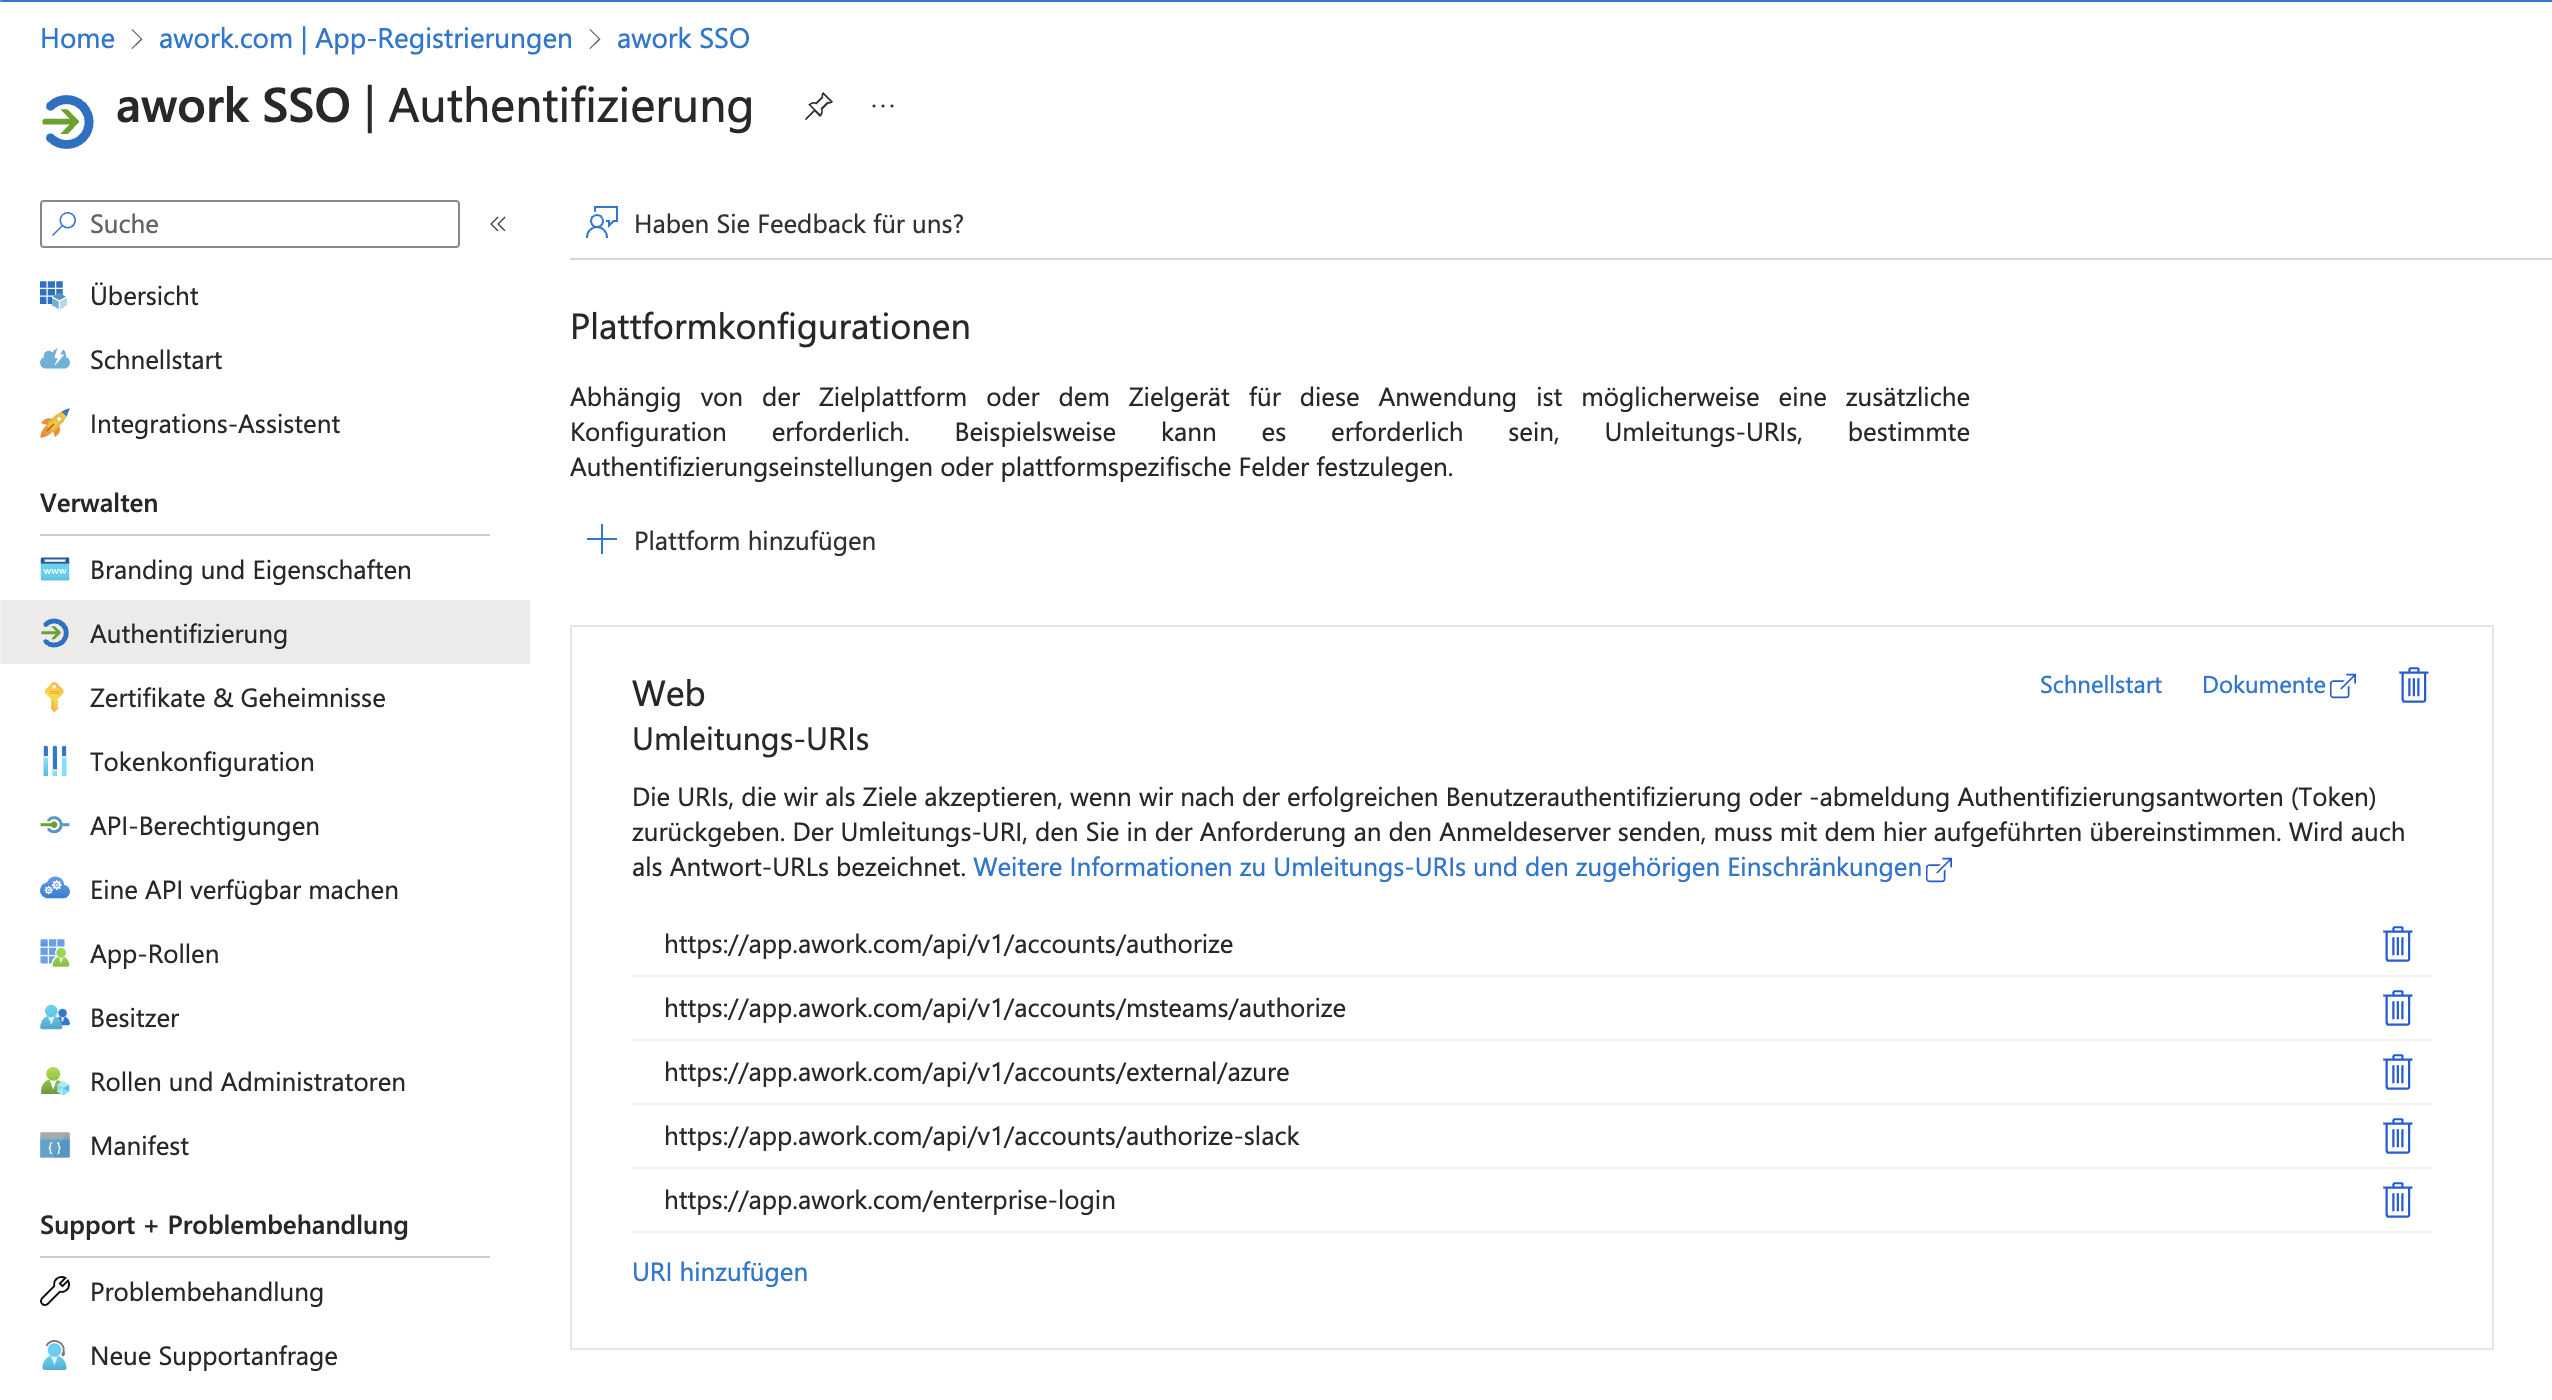
- Under Authentifizierung, add the following redirect URLs for a Web platform:
https://app.awork.com/enterprise-login https://app.awork.com/api/v1/accounts/authorize-slack https://app.awork.com/api/v1/accounts/external/azure https://app.awork.com/api/v1/accounts/msteams/authorize https://app.awork.com/api/v1/accounts/authorize
 )
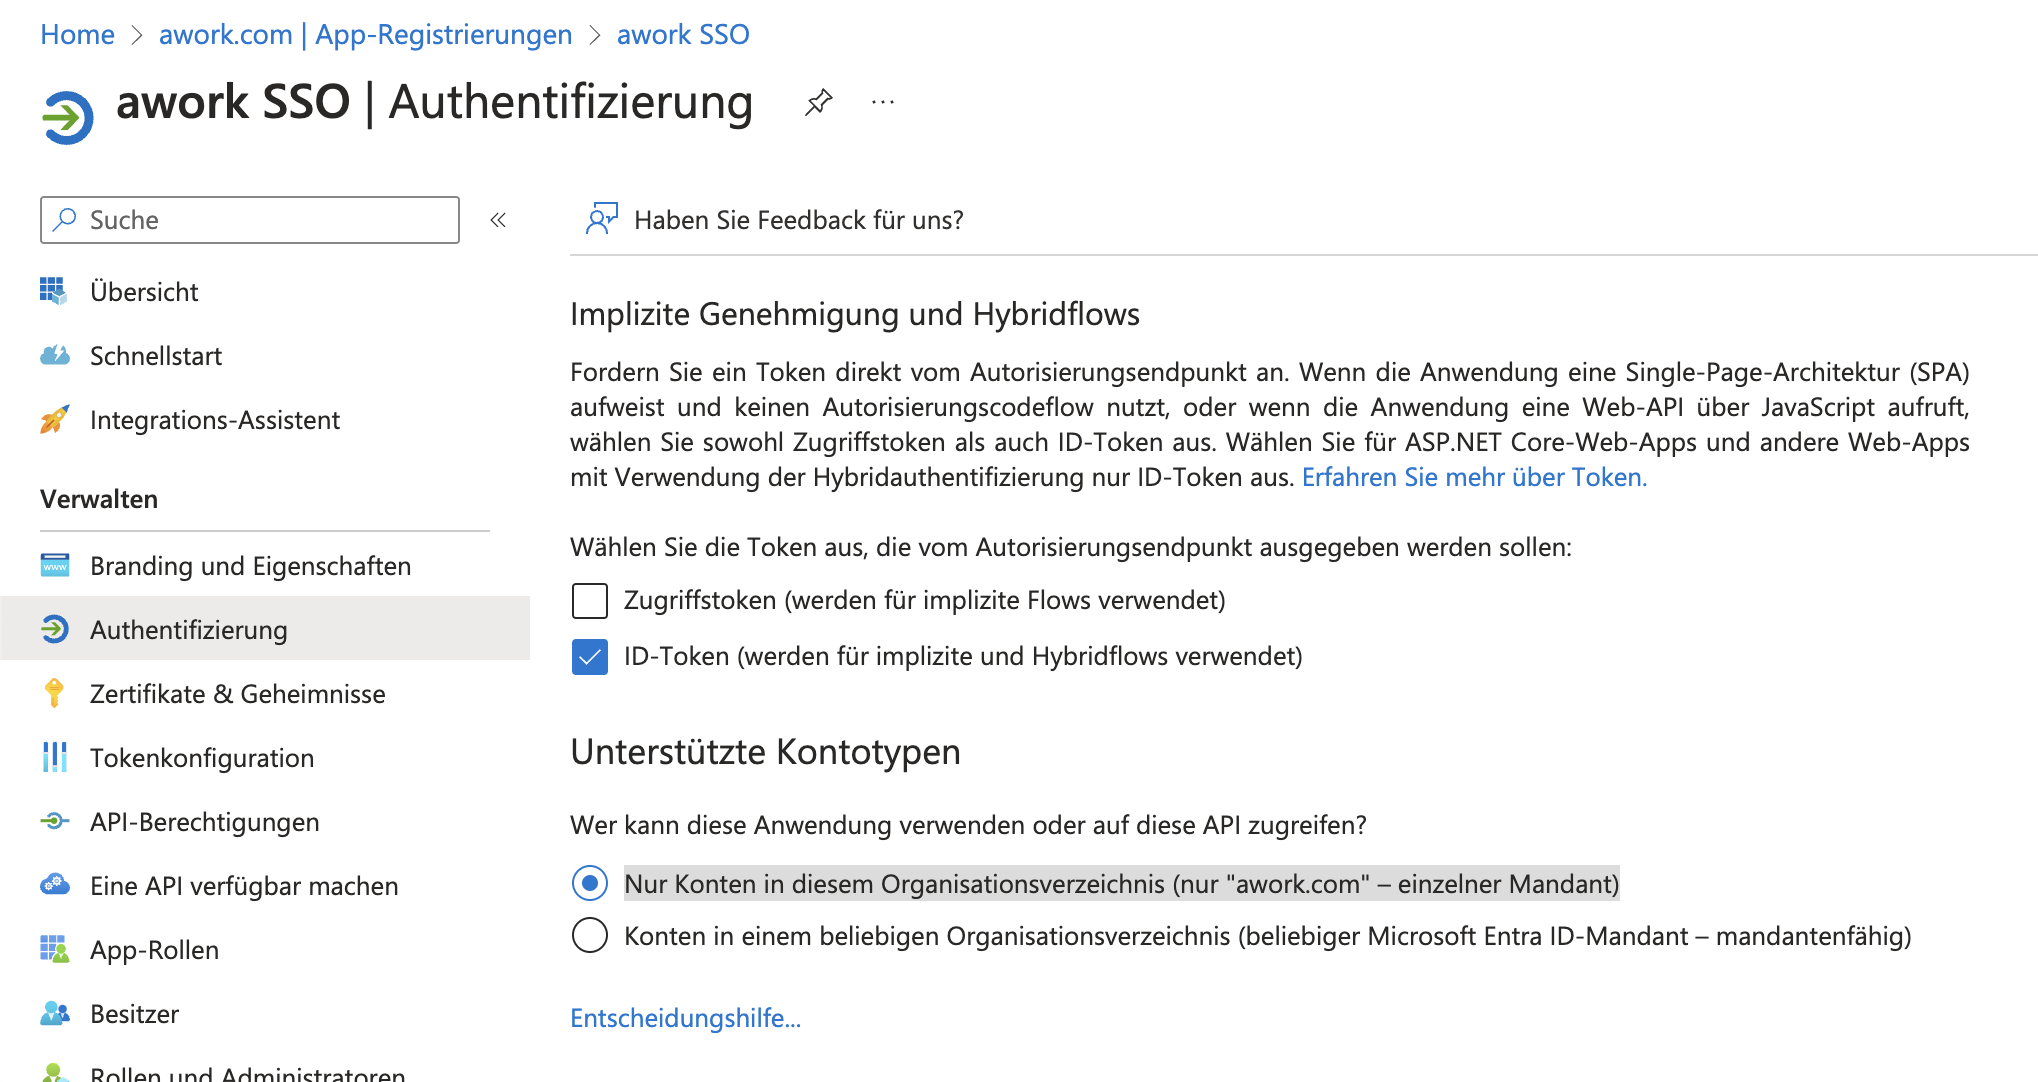
Under Implizite Genehmigung und Hybridflows, make sure ID-Token is checked. Under Unterstützte Kontotypen, select Nur Konten in diesem Organisationsverzeichnis (nur "deine Domain" - einzelner Mandant).
 )
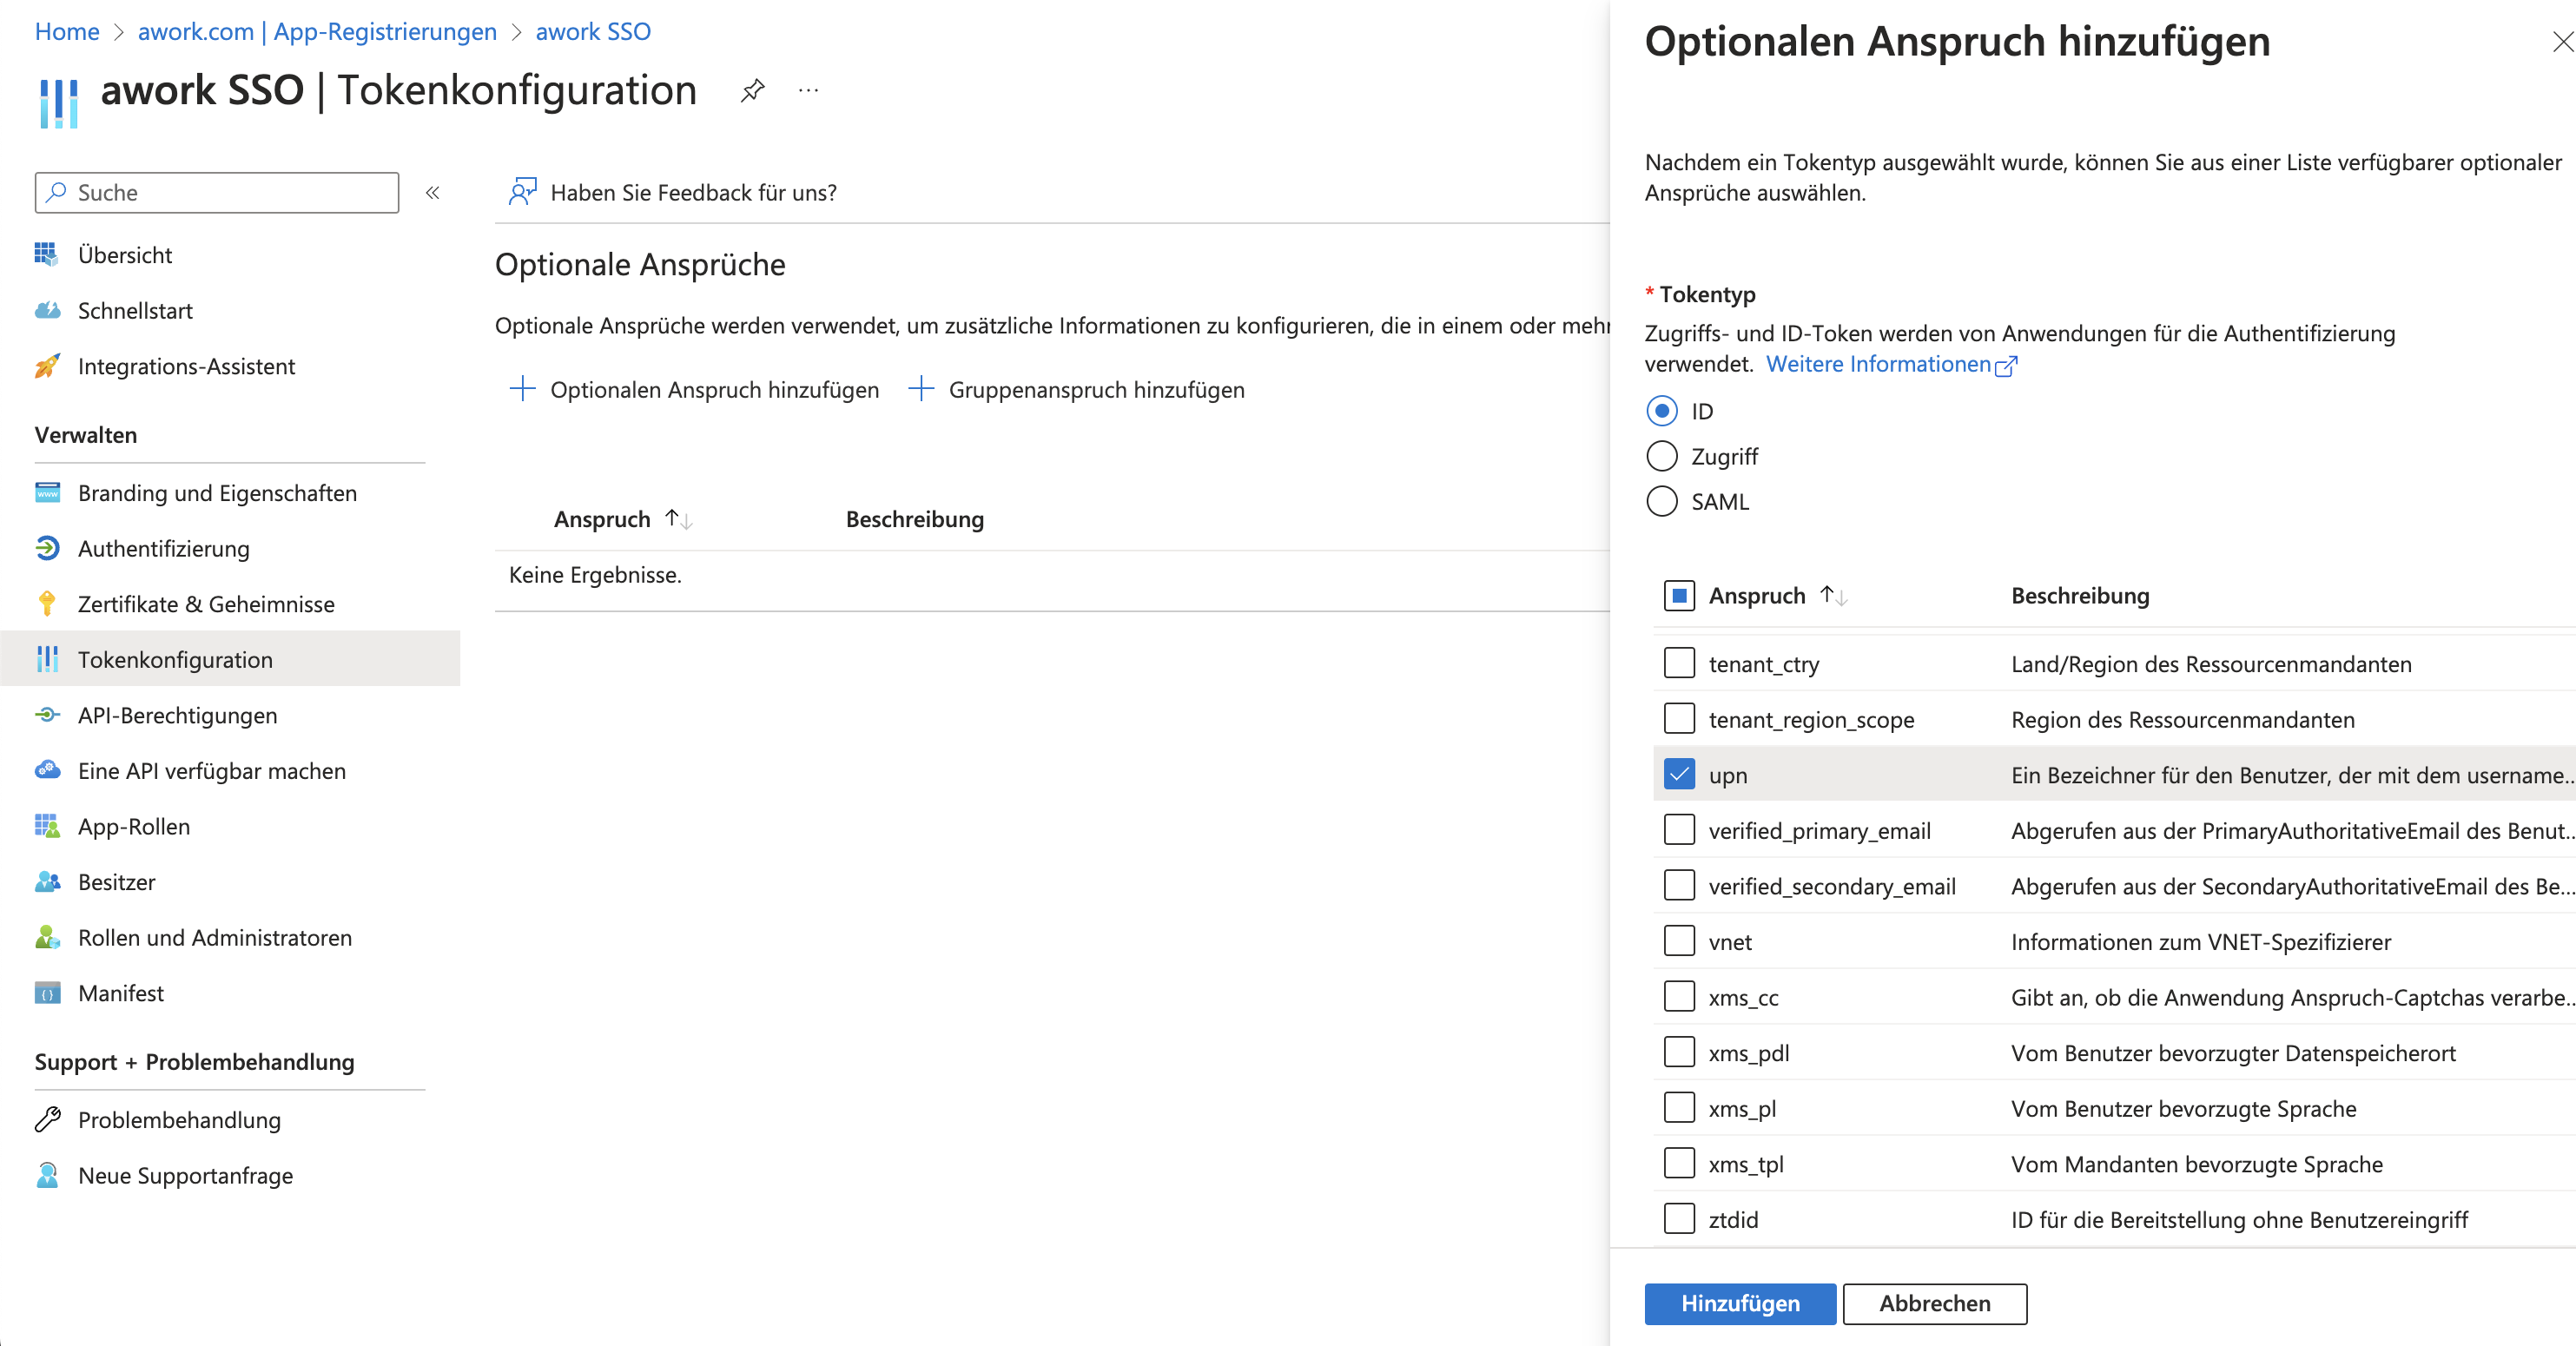
By default, the login flow uses the preferred_username claim from the Entra user. If you want to use UPN instead, you can configure UPN as an optional claim in Tokenkonfiguration:
- Token type:
ID - Claim:
upn
Then click Hinzufügen.
 )
Important: UPN is only supported as an optional claim for app registrations for tenants, not for personal Microsoft accounts. Make sure this is configured correctly under Authentifizierung.
Make sure the email address returned by Entra ID matches the email address of the user's awork account. In tenants where userPrincipalName differs from the actual email address, the correct email address may come from mail or another suitable attribute.
Configure SSO with GSuite (Google IAM)
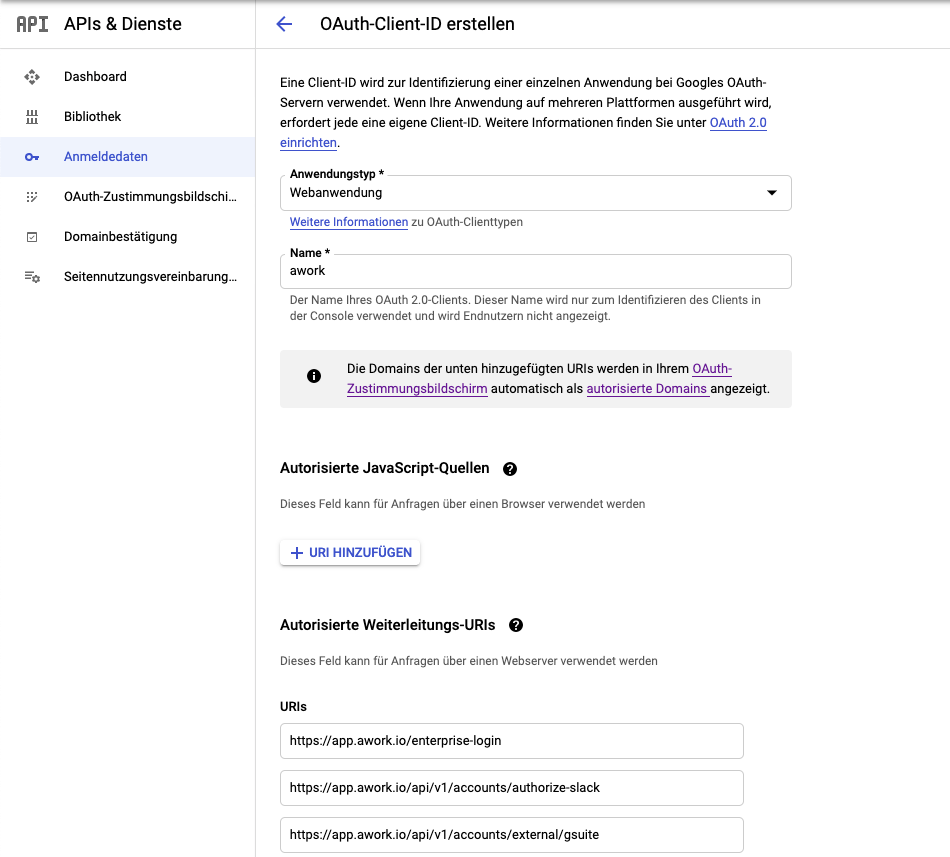
- Go to https://console.cloud.google.com/apis/credentials and select your project.
- Click Anmeldedaten erstellen and select OAuth-Client-ID.
- Select Webanwendung as the type.
- Enter a name, for example, awork.
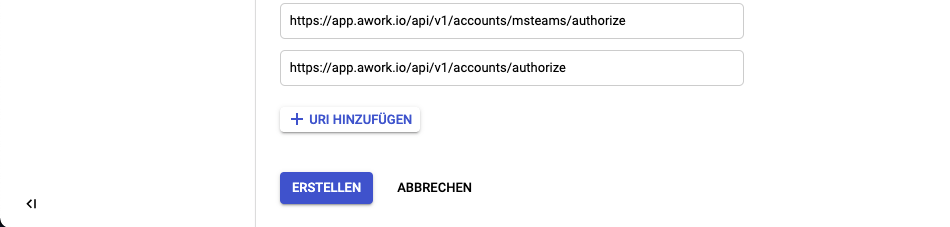
- Under URIs, add the following redirect URLs: https://app.awork.com/enterprise-login https://app.awork.com/api/v1/accounts/authorize-slack https://app.awork.com/api/v1/accounts/external/gsuite https://app.awork.com/api/v1/accounts/msteams/authorize https://app.awork.com/api/v1/accounts/authorize
- Save by clicking Erstellen.
- On the right, you'll find the Client-ID and Clients Schlüssel (Client-Secret). Enter these in awork.
 )
 )
You can find more information about SSO with GSuite here.
Configure SSO with Keycloak
Important: Please contact our Support if you'd like to set up SSO via Keycloak, as this option isn't currently available in the web app.
To set up Keycloak SSO via OpenID Connect:
-
Log in to your Keycloak Admin Console.
-
Go to Clients.
-
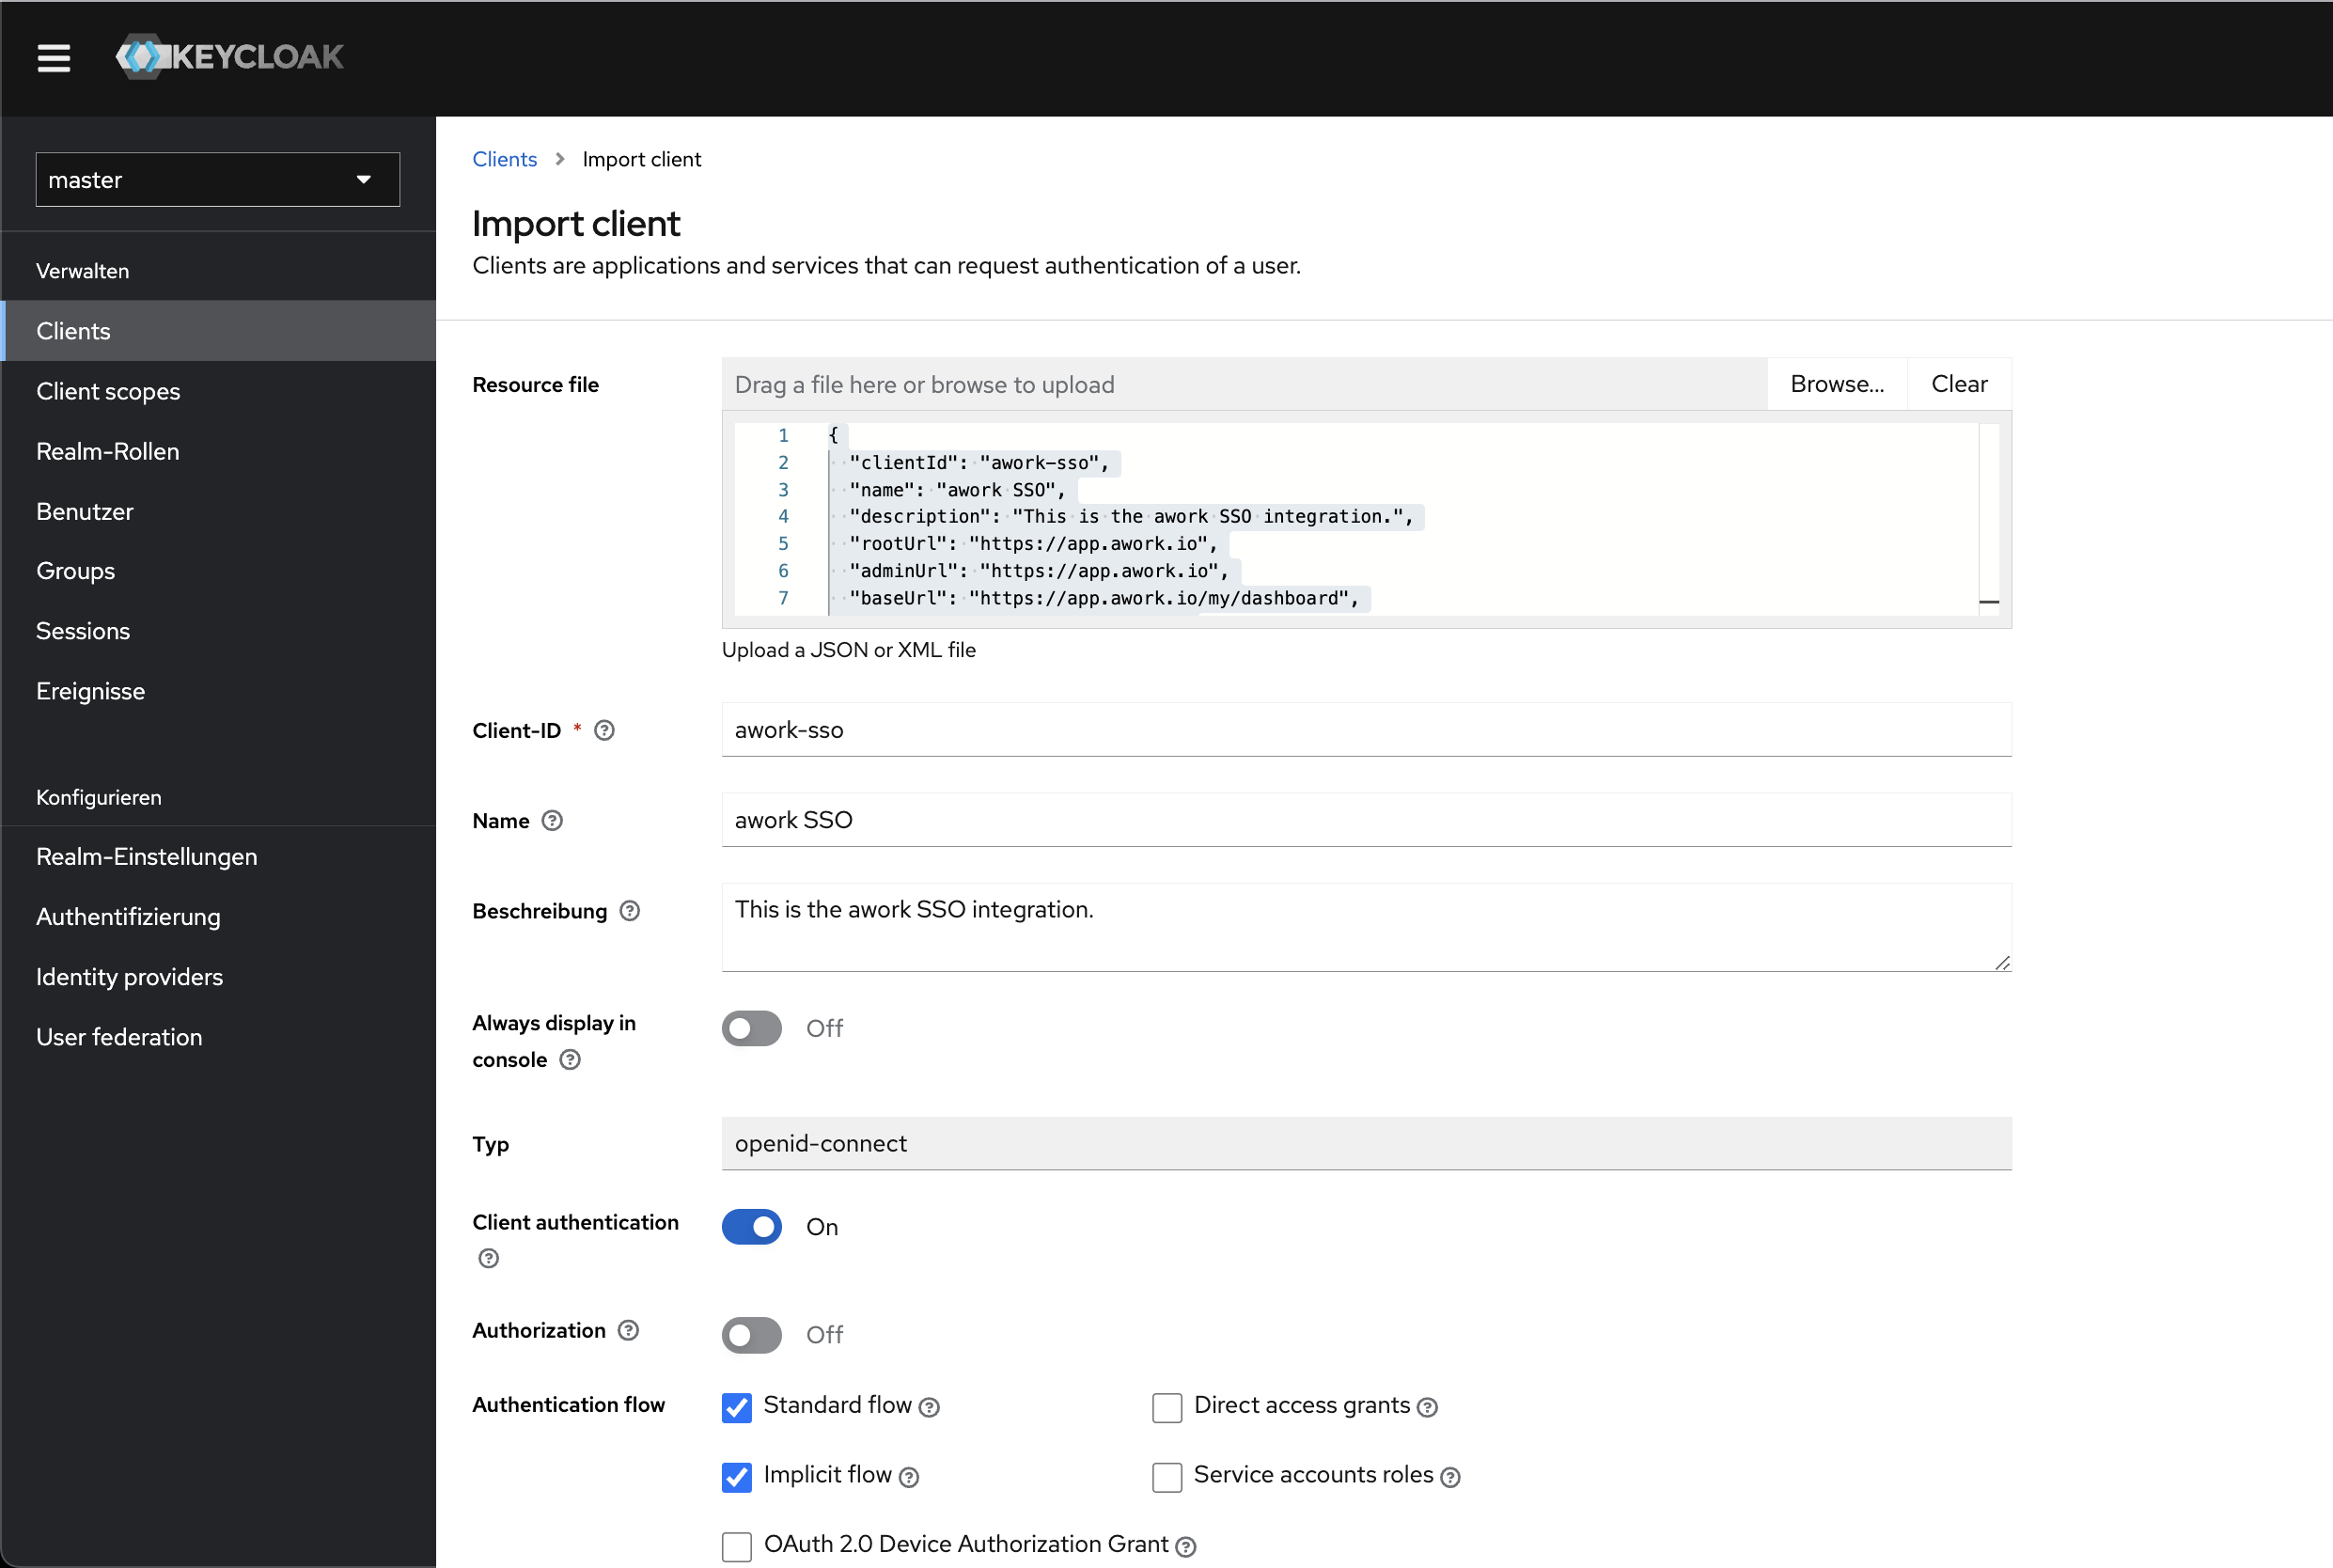
Download the client configuration file: Keycloak awork Client Configuration
-
Drag the file into the resources field to import the required settings.
-
Save the new client.
 )
-
In the client details, go to the Passwörter tab and copy the client secret.
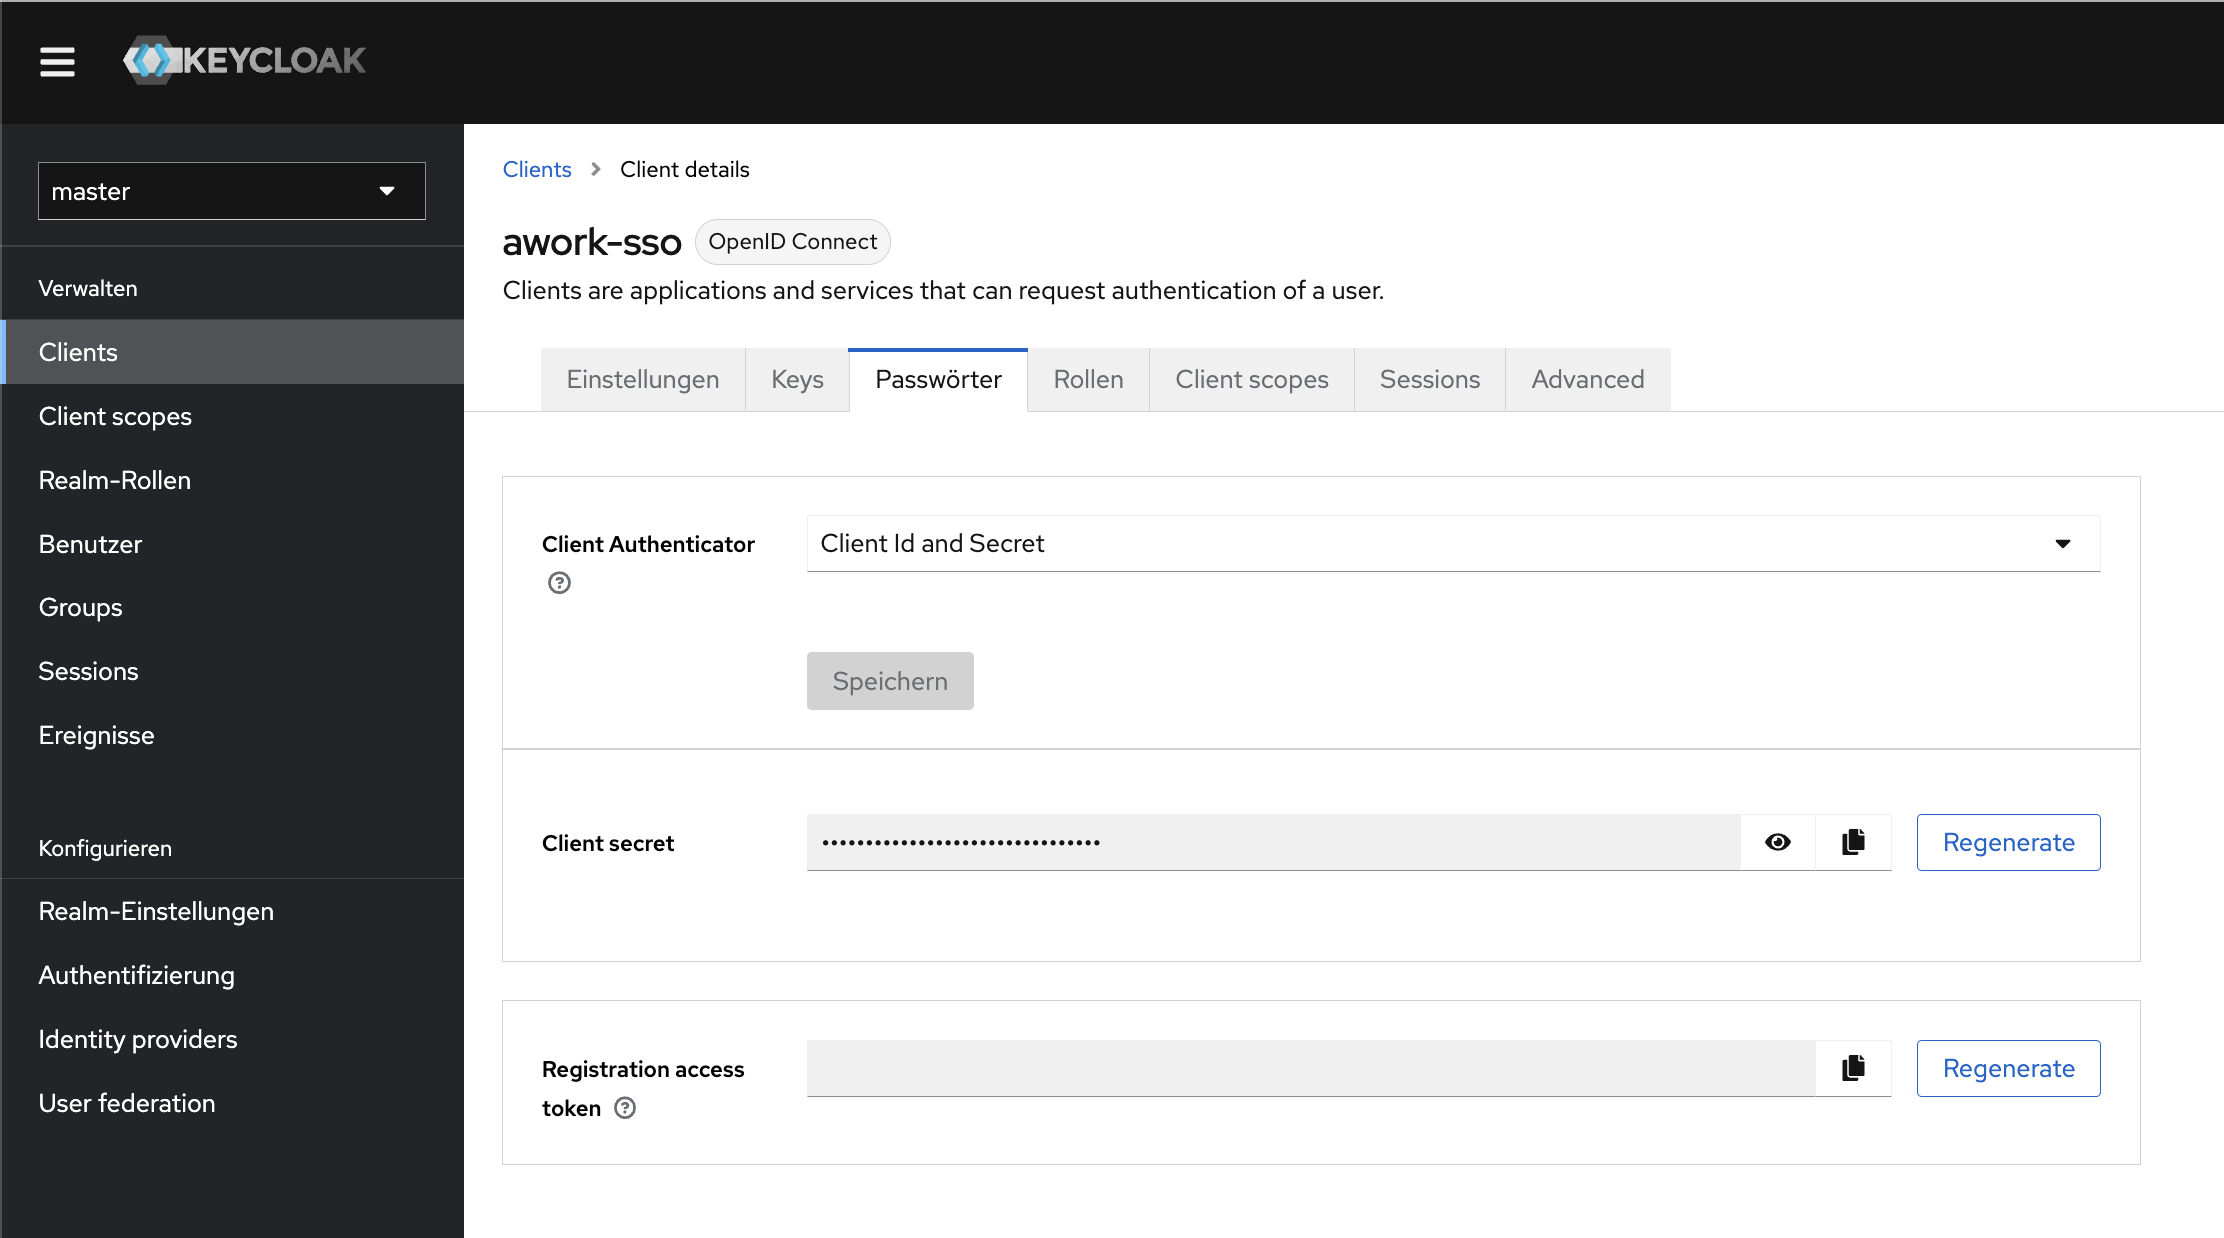 )
-
In Realm-Einstellungen, you'll find the
.well-known/openid-configurationlink at the bottom of the General settings (* OpenID Endpoint Configuration*). The URL usually looks like this: https://{your-keycloak-url}/realms/master/.well-known/openid-configuration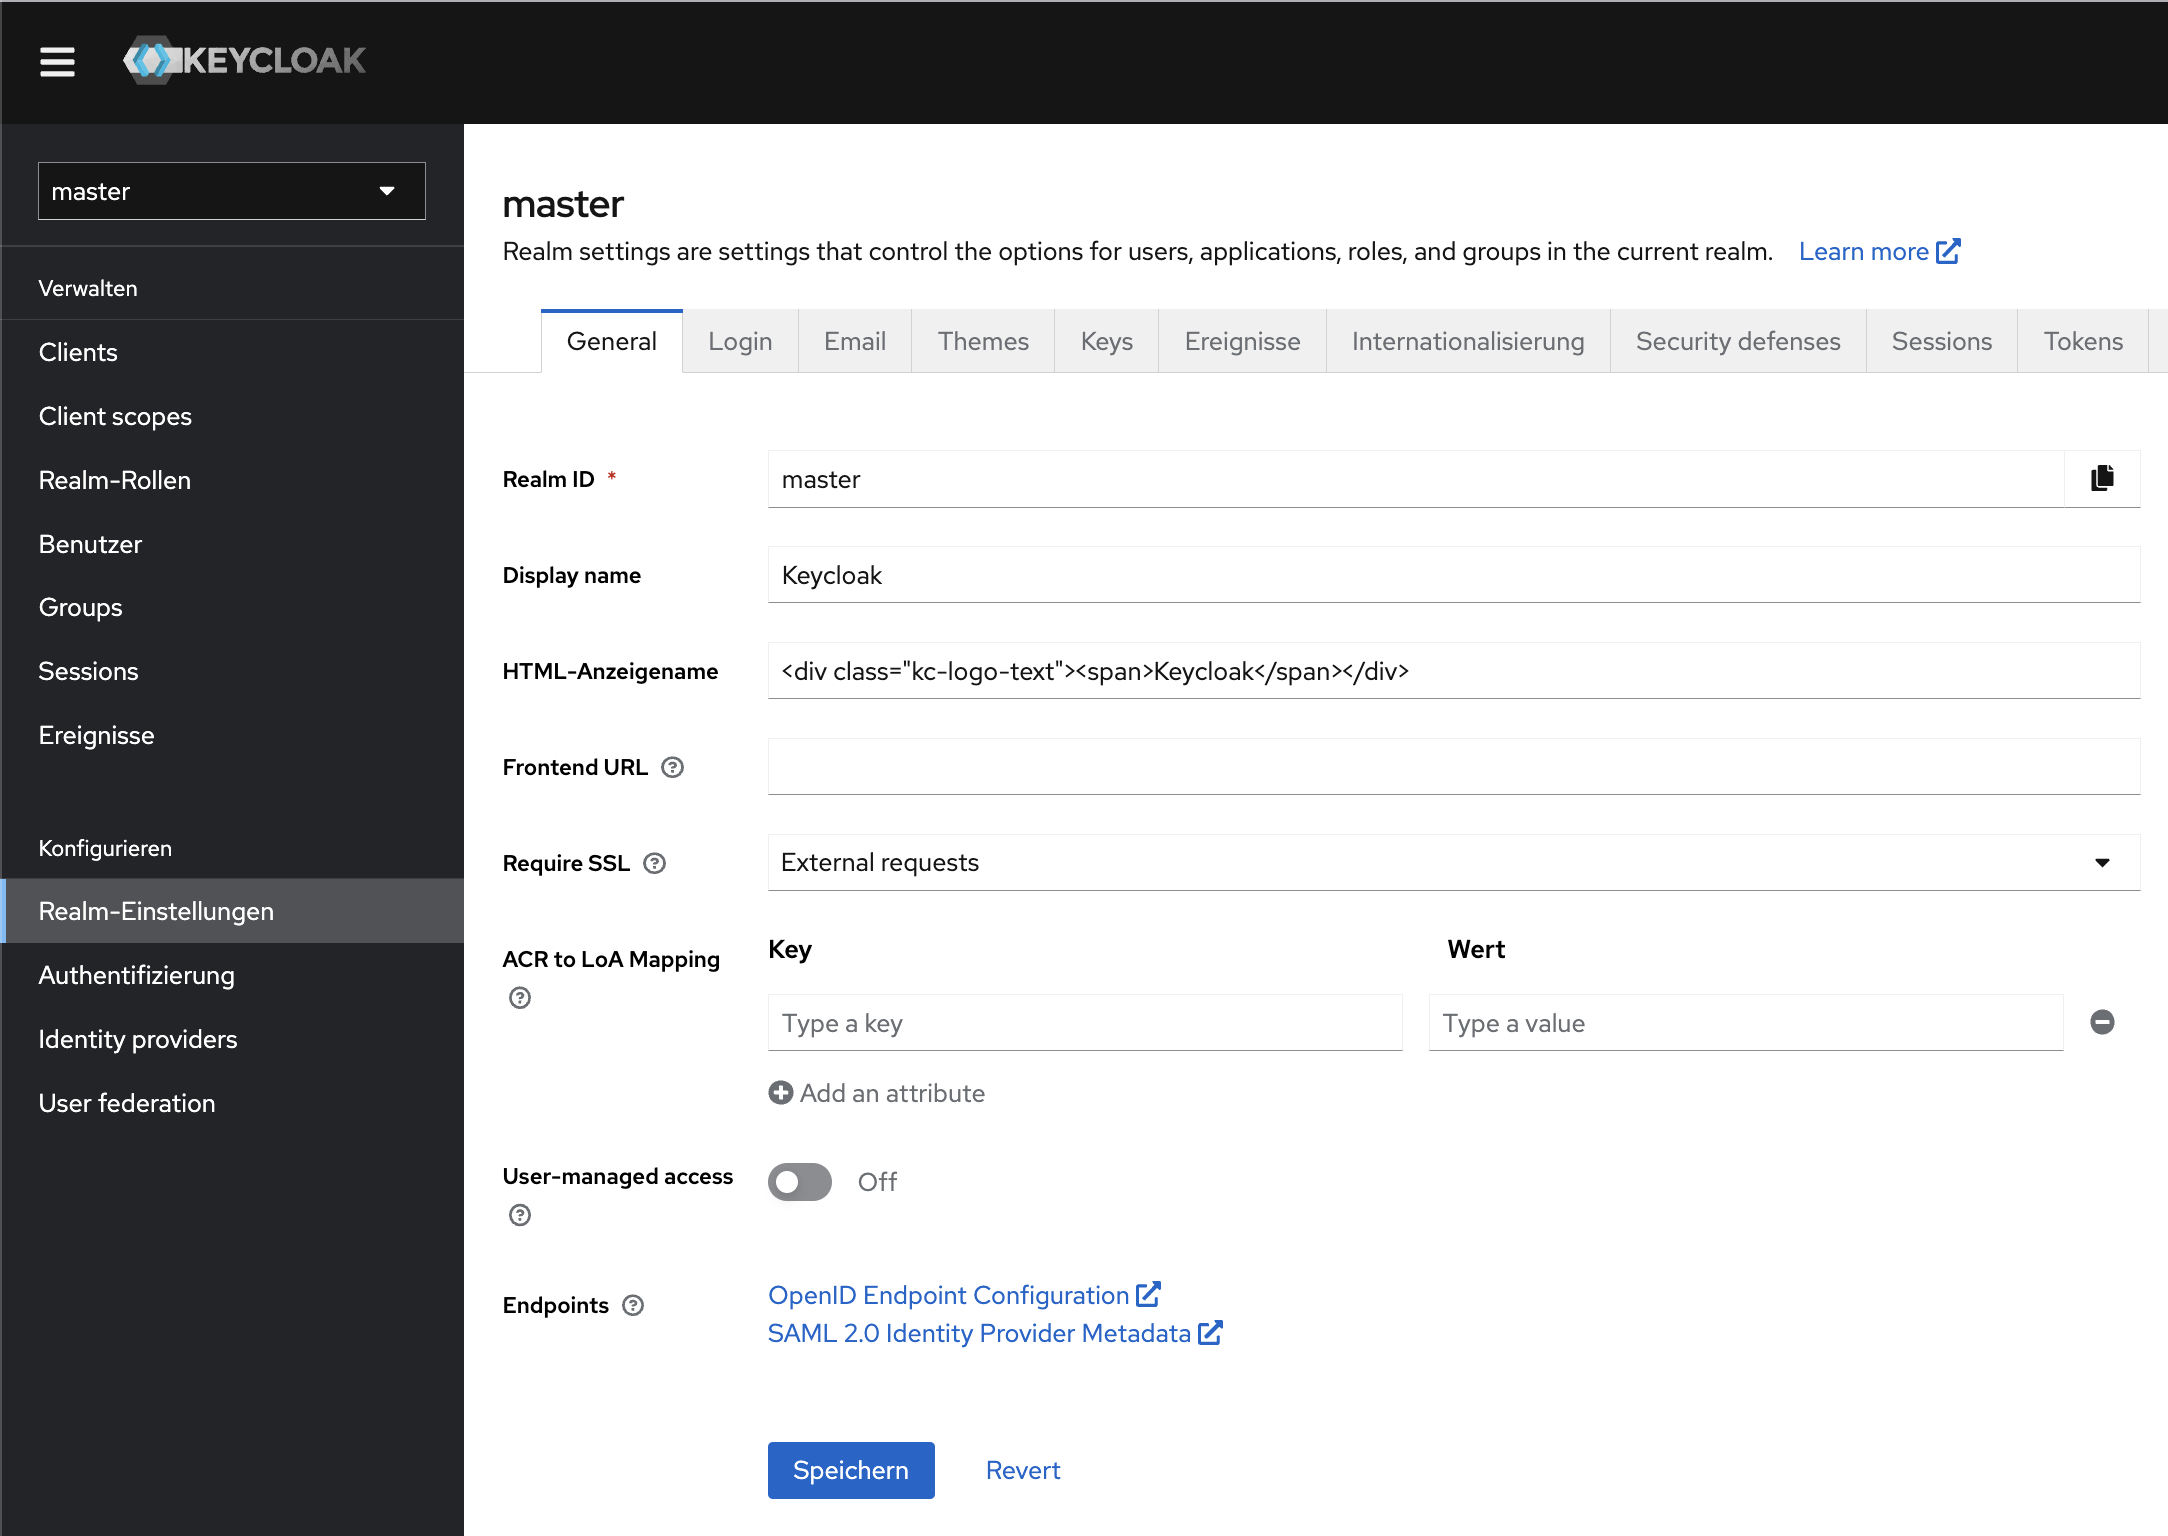 )
-
Contact Support with your Client ID, Client Secret, and
.well-known/openid-configurationURL so we can set up the integration for you.
Important: The .well-known/openid-configuration URL must remain available at all times to prevent errors when signing in with SSO.
Configure your own SSO providers (OpenID Connect)
awork also supports other SSO providers that use OpenID Connect.
To set this up, you'll need the full OpenID Configuration URL (for example, https://custom-domain.com/.well-known/openid-configuration), your Client ID, and your Client Secret.
Sign in via SSO at app.awork.com
- Go to app.awork.com.
- Select Einloggen mit SSO.
- Enter your workspace subdomain.
You'll be redirected to the SSO login screen or, if you're already signed in, directly to your awork dashboard.
Tips and notes
SSO matches users based on their email address. It doesn't automatically create new awork accounts. The email claim sent by your identity provider must match the email address of the existing awork account.
This means a user must already exist in awork before they can sign in via SSO.
Note: Permissions, users, and groups aren't managed through SSO. You'll continue to manage this information in awork or via SCIM, if SCIM is set up.
Disable other login methods
Once SSO is configured, you can disable and hide other login methods (email and password, as well as social login via Google and Microsoft).
- Go to Einstellungen > Allgemein.
- Disable the other login options.
We recommend doing this only if there are no external or guest users in your workspace who aren't managed through identity management.
In particular, check for external and guest users before disabling email and password login and social login. Otherwise, these users may be affected by the sign-in restrictions even though they aren't managed by your identity provider.
Note: If you remove the SSO settings in awork, email and password login will automatically be re-enabled so you can always sign in with your admin account.
Global login vs. workspace login
If you've disabled email and password login and/or social login, these options will still appear on the global page at app.awork.com. They'll only be hidden on your workspace page, YOUR-WORKSPACE-SUBDOMAIN.awork.com.
You still won't be able to sign in via the global page. Use YOUR-WORKSPACE-SUBDOMAIN.awork.com to sign in via SSO.
When SSO is configured, Einloggen mit SSO will also appear on YOUR-WORKSPACE-SUBDOMAIN.awork.com. You'll be redirected to the SSO login screen or directly to your dashboard.
FAQ
Is SSO available on every plan?
No. SSO is only available on the awork Enterprise plan.
Does awork support SAML 2.0?
No. awork doesn't support SAML 2.0. Instead, it uses OpenID Connect based on OAuth 2.0.
Can my identity provider manage permissions, users, or groups in awork?
No. SSO only manages sign-in. Permissions, teams, roles, and other user data aren't automatically managed in awork through SSO. SSO matches users based on their email address and doesn't automatically create new awork accounts. The email claim sent by your identity provider must match the email address of the existing awork account. This means a user must already exist in awork before they can sign in via SSO.
What happens if I remove the SSO settings after disabling other login options?
Email and password login will automatically be re-enabled, so you can always sign in with your admin account.
Can I set up SSO with Keycloak in the awork web app?
Not yet. Please contact Support to set up Keycloak SSO, as this isn't currently possible in the web app. This feature is coming soon.
 Powered by happysupport.ai